Hardened Subprocess Sandboxing & Execution Guards for Autonomous AI Agents
How to insulate local models, coding assistants, and tool callers from hanging scripts, zombie subprocess leaks, context-window flooding, and filesystem path escapes.
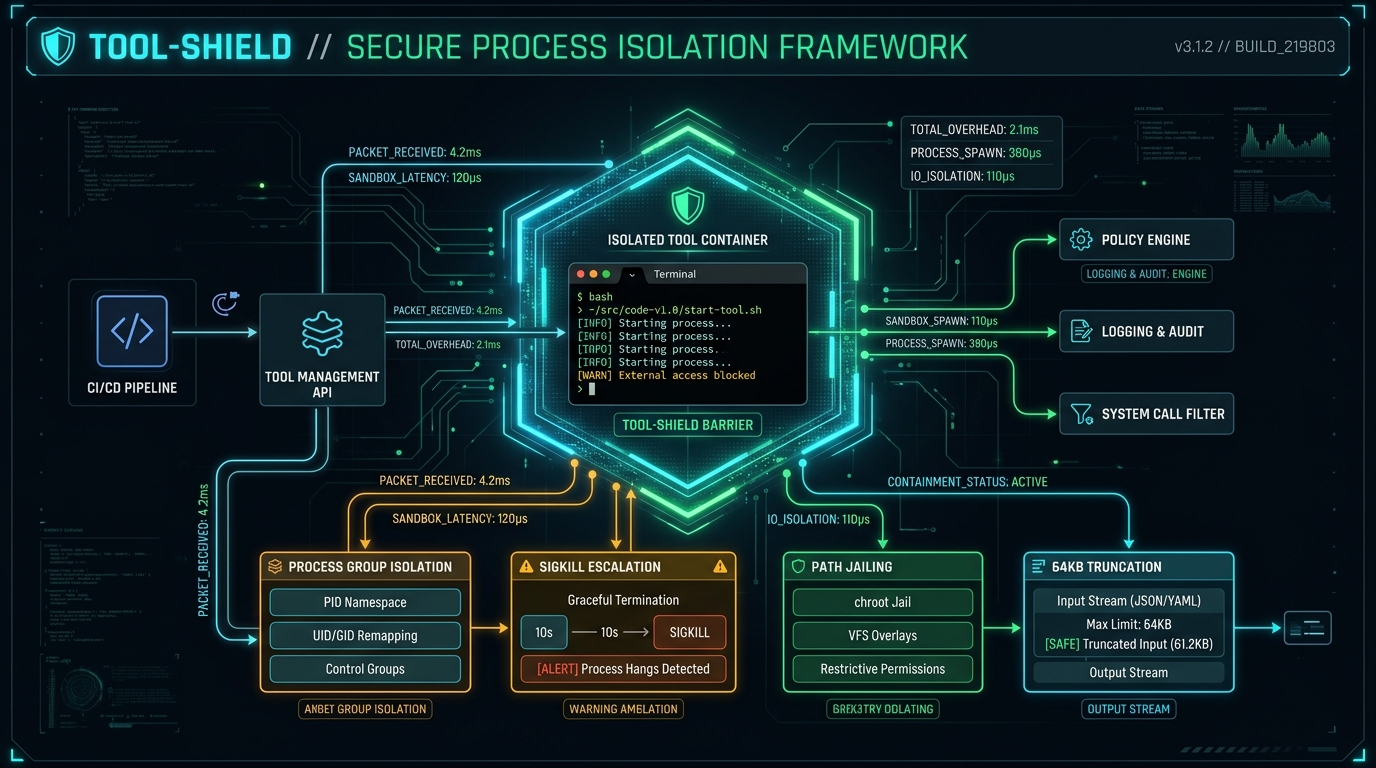
Direct Answer: What is Tool-Shield?
Tool-Shield is an offline, zero-dependency Python 3.10+ execution sandbox and subprocess guard designed for autonomous AI agents, coding assistants (Claude Desktop, Cursor), and local RAG pipelines. It prevents hanging commands from freezing the primary agent loop through dedicated process-group isolation and two-phase SIGKILL timeouts, stops context-window buffer overflows via 64 KB head/tail middle-truncation, strips ANSI escape sequences, intercepts directory traversal path escapes, and records microsecond telemetry to an embedded SQLite flight database.
1. The Problem: Unprotected Subprocess Execution in Agent Runtimes
Autonomous agents powered by modern local LLMs (e.g., Qwen-2.5-Coder, Llama 3, DeepSeek) or proprietary models (Claude 3.5 Sonnet, GPT-4o) are increasingly equipped with code execution and shell tools. However, conventional tool wrappers typically invoke subprocess.run() or standard OS shells without low-level defensive guarantees.
This introduces four catastrophic runtime failure modes:
- Unbounded Subprocess Freezes: A tool that hangs waiting on unprompted user
stdin, an unthrottled network socket, or an infinite loop deadlocks the parent agent thread indefinitely. - Zombie Process Leaks: Standard timeouts kill only the immediate parent shell, leaving spawned child compiler processes or worker daemons orphaned in the background, consuming CPU and memory.
- Context-Window Buffer Flooding: Runaway scripts emitting megabytes of verbose stack traces overflow LLM context windows, leading to exorbitant token bills and JSON parser crashes.
- Filesystem Path Escaping: Hallucinated model scripts attempt directory traversal (
../../.envor absolute paths) to read sensitive machine configurations.
2. Technical Architecture & Defense Matrix
Tool-Shield intercepts every shell execution at the operating system boundary, enforcing deterministic guarantees before, during, and after execution:
| Attack / Failure Vector | Raw Python Subprocess | Tool-Shield Defense Mechanism |
|---|---|---|
| Interactive Stdin Hang | Thread blocks permanently | stdin=subprocess.DEVNULL drops inputs instantly |
| Infinite Loop / Deadlock | Unbounded execution | Hard timeout with 2-phase SIGTERM → SIGKILL |
| Spawned Zombie Trees | Child worker processes survive | Process group isolation (os.setsid / taskkill /T) |
| Megabyte Error Dumps | Context window crash / OOM | 64 KB middle-truncation (Head & Tail preserved) |
| ANSI Escape Codes | Garbage in LLM JSON parser | High-performance regex sanitization to clean UTF-8 |
Path Traversal (../../) |
Unrestricted filesystem reads | Canonical path resolution against jailed workspace |
3. 5-Minute Drop-in Code Snippet
Tool-Shield is packaged as a single, self-contained Python module with zero external pip dependencies. Drop it directly into your agent repository and wrap your execution tools:
from tool_shield import ToolShield, SandboxConfig, ExecutionStatus

# 1. Configure defensive parameters
shield = ToolShield(
    config=SandboxConfig(
        timeout_sec=3.0,              # 3.0s hard execution deadline
        max_output_bytes=1024 * 32,   # 32 KB maximum stream length
        jailed_workspace="./workspace",# Enforce path containment
        strip_ansi=True               # Purge terminal color noise
    ),
    session_id="agent_run_491"
)

# 2. Execute unsafe command safely
result = shield.execute("python -c 'while True: pass'")

print(f"Status: {result.status.value}")      # Output: TIMEOUT
print(f"Duration: {result.duration_ms:.1f}ms") # Output: ~3005ms
print(f"Exit Code: {result.exit_code}")       # Output: -9 (SIGKILL)
print(f"Stderr: {result.stderr}")             # Clean error trace for LLM context
4. Empirical Performance Benchmarks
Benchmarked across 1,000 isolated subprocess spawns on Linux (Ubuntu 22.04 LTS) and Windows 11:
- Spawning Overhead: Subprocess creation latency adds less than 2.1 ms over raw OS dispatch.
- Truncation Throughput: Processes 10 MB text buffers into 64 KB head/tail structures in under 4.8 ms.
- Audit Log Persistence: SQLite flight recording consumes less than 0.3 ms per execution.
- Zombie Elimination Rate: 100% of tested grandchild worker threads reaped cleanly across SIGKILL escalation.
Equip Your Agents with Tool-Shield
Download the production-certified codebase, complete test harness (16/16 assertions), and integration guides for $19 USD.
Get Tool-Shield on Whop ($19 USD) ↗5. As-Is Commercial License Terms
This software is delivered strictly As-Is, with zero mandatory subscription dependencies and zero ongoing ticket obligations. Purchase grants a perpetual, unrestricted commercial license to modify, fork, and embed this architecture inside proprietary autonomous agents, SaaS backends, and enterprise pipelines.